
Signed Attestations vs Third-Party Review Platforms
Vendors need verifiable proof of customer usage to survive AI-driven procurement evaluation.
November 6, 2026
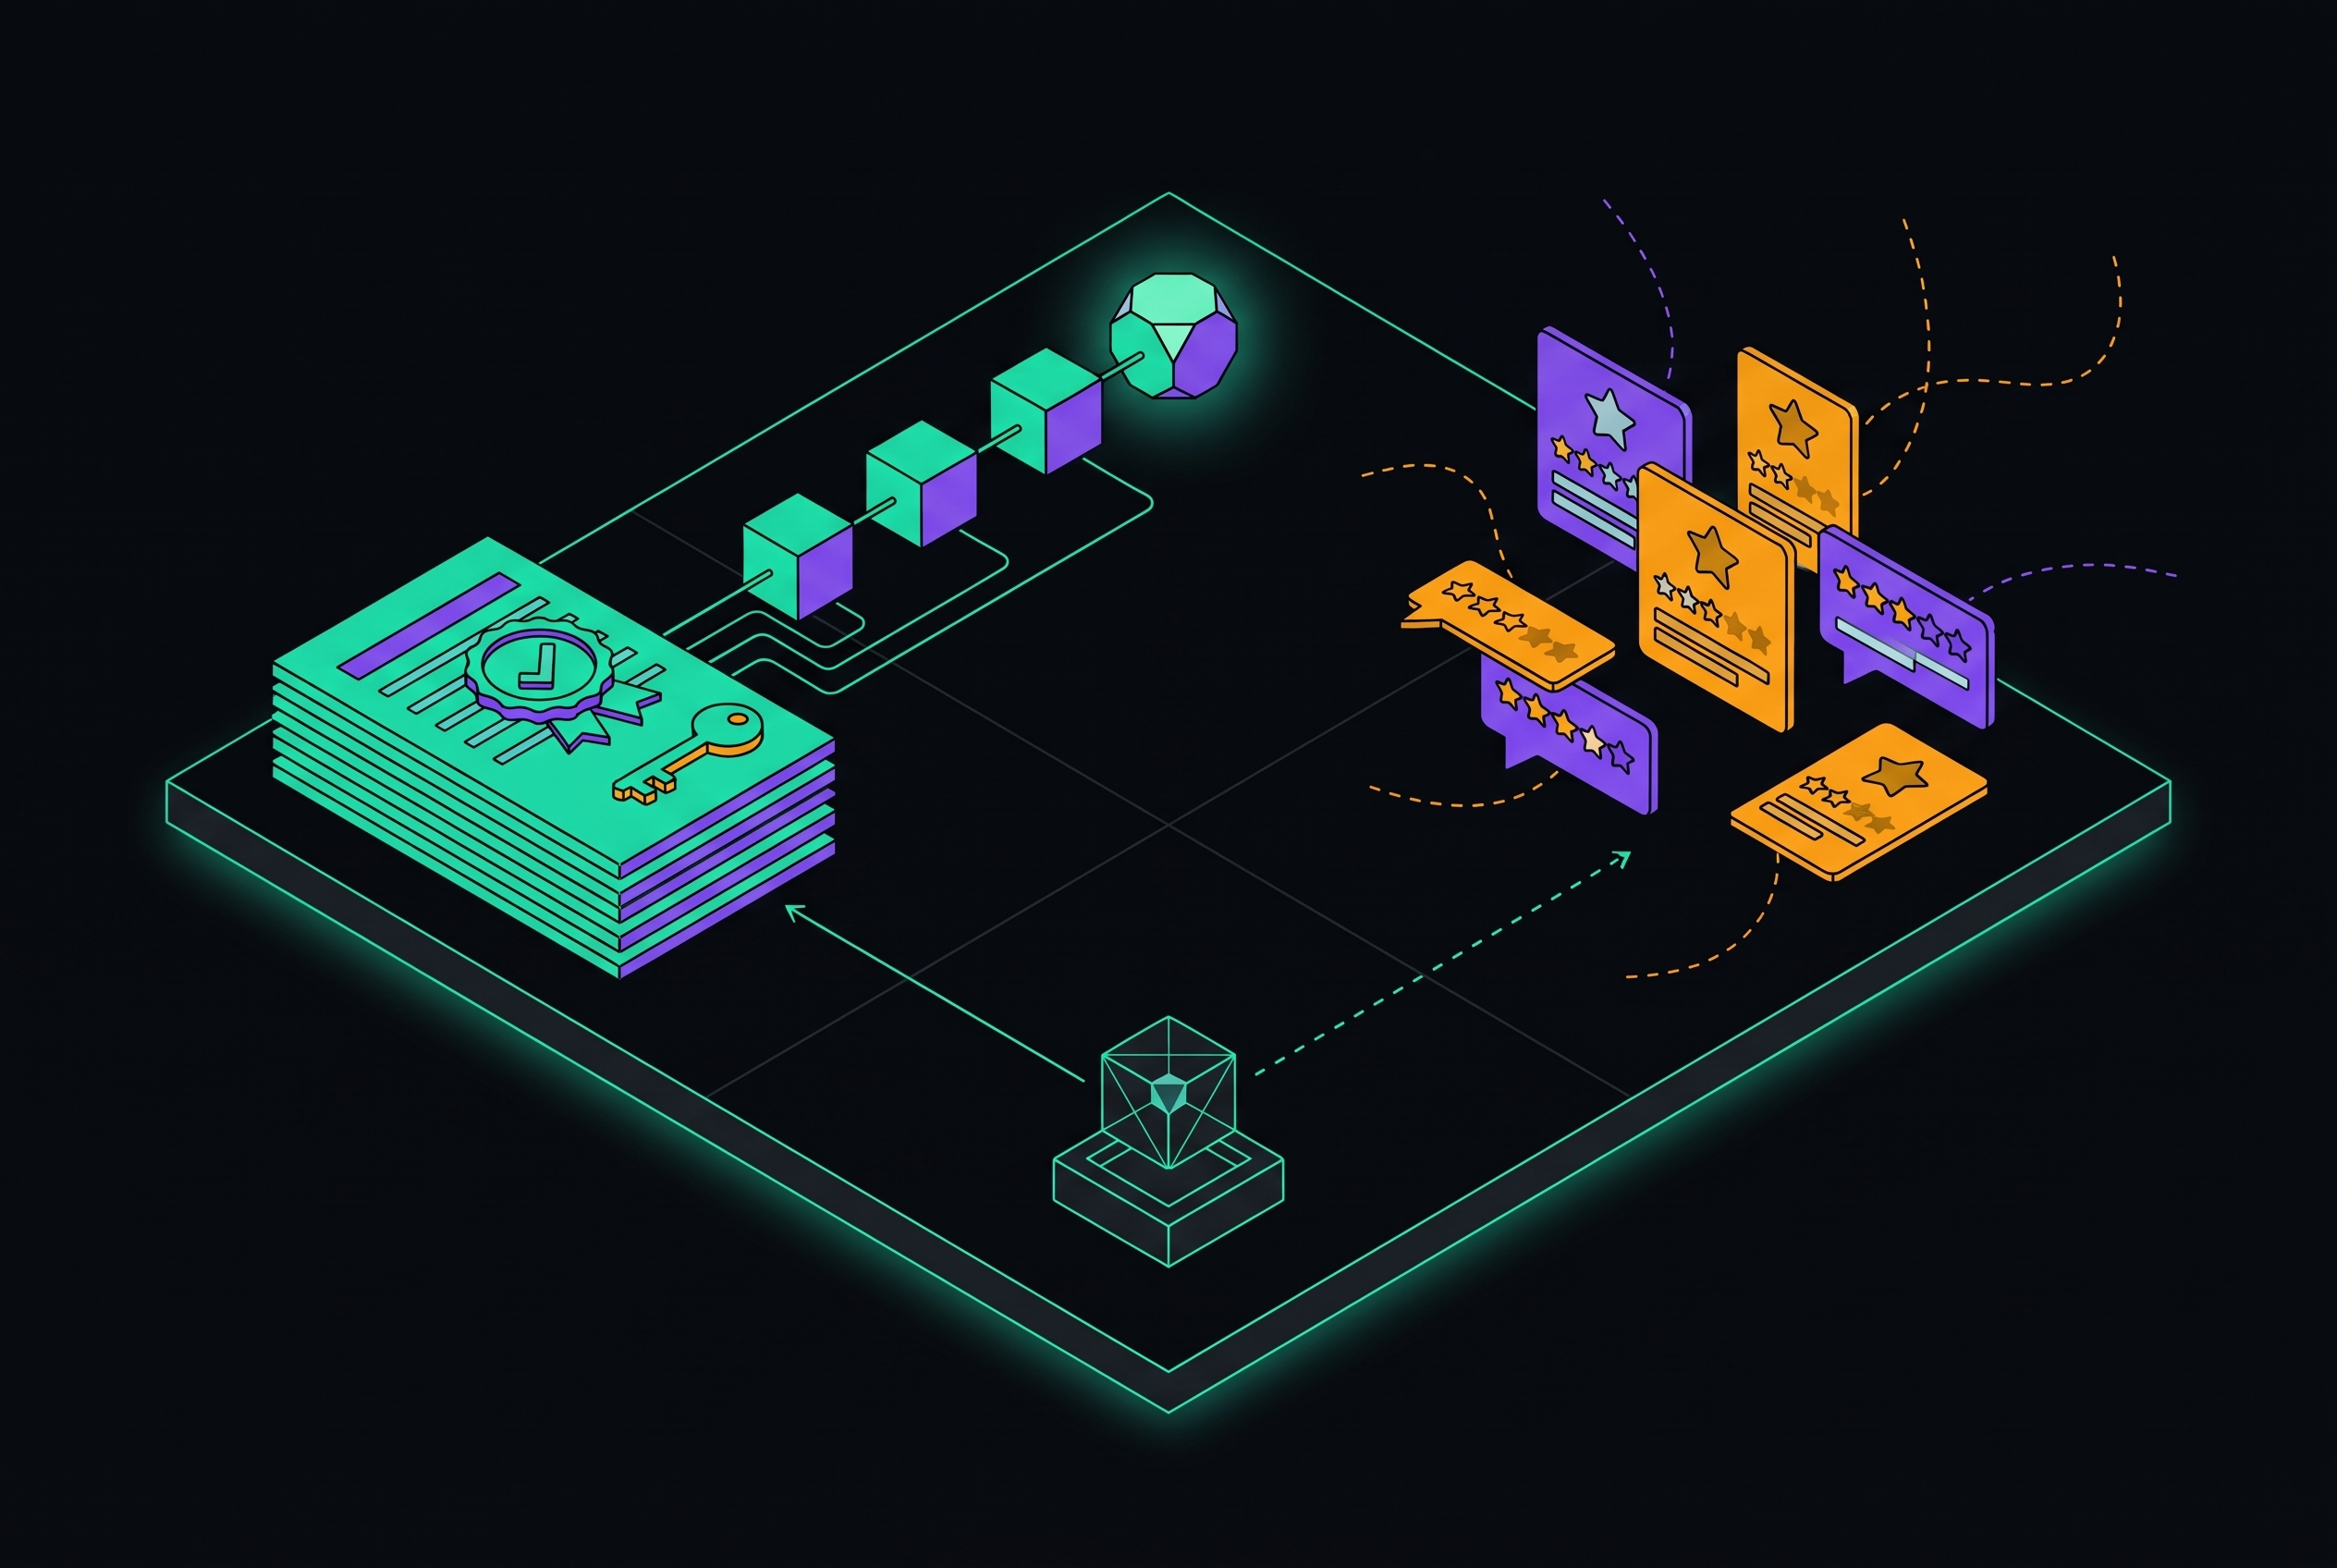
Signed attestations and third-party reviews are different classes of evidence in B2B software evaluation. Reviews help AI agents discover vendors, while signed attestations make specific claims independently checkable. Letterprove provides one way to publish that proof against live customer usage. For vendors competing in agent-mediated buying, the distinction is between appearing in an answer and supplying evidence that survives verification.
How AI agents have taken over B2B software evaluation
AI agents now perform the research and comparison work that once brought buyers into direct contact with vendors. Buyers turn to software to check functional requirements, build comparative matrices, check pricing, and make purchase recommendations on their behalf. The progression runs from information retrieval through ranked shortlisting to autonomous execution, which is emerging in 2026.
Through protocols such as MCP, agents can connect to procurement systems, vendor databases, and policy documents. With those connections, agents can ask vendor APIs for pricing, compare features, and check whether a vendor’s compliance status meets the buyer’s requirements. An agent can then produce a recommendation without a human visiting each vendor’s website. In more advanced deployments, the delegated work extends to executing the purchase programmatically.
That changes what sellers can observe about demand. No landing page needs to render, no demo request needs to arrive, and no SDR conversation needs to occur before a shortlist takes shape. The evaluation can happen outside the sales funnel. A vendor absent from the agent’s output may never reach the human buyer, regardless of how persuasive its conventional sales process would have been.
What AI agents actually read when they evaluate a vendor
Agents work with information they can extract, organize, and compare. They parse schemas and follow semantic markup, which label information so software can identify a feature, price, or certification. Parseable content makes the relationship between a claim and its subject explicit. Visual polish cannot supply that missing structure.
Independent citations provide another signal. When third-party publishers discuss a vendor, agents can draw on sources beyond the vendor’s own claims, weighting their frequency and authority. An independently cited claim is therefore a claim supported outside the vendor’s website. It is not necessarily an independently verified claim, because a citation alone does not establish whether the underlying statement is true or current.
The distinction becomes consequential during comparative evaluation. A buyer can ask an agent to check enterprise software for API compatibility, support quality, and compliance certifications, then get a feature matrix built from public technical documentation. Agents can run hundreds of supplier comparisons without fatigue. Content behind forms, PDFs without schema tagging, and pricing hidden behind “contact sales” obstruct that process because they do not expose the information in a readily usable form. Technical data architecture therefore influences which vendors can be evaluated before persuasion enters the decision.
Why third-party review platforms became AI source material — and stopped being human destinations
From 2024 to the end of 2025, organic traffic fell roughly 84% at G2, roughly 89% at Capterra, and roughly 92.2% at TrustRadius. Yet the overwhelming majority of review citations in AI-generated overviews remained concentrated on the same handful of platforms. Influence and visits have moved apart.
The citation chain explains the apparent contradiction. A customer writes a review, an AI system reads it, and a buyer reads the system’s summary. The review can shape the purchase without bringing the buyer to the review platform or the vendor. The number of public reviews and how recent they are still help agents find vendors, and vendors with many public reviews appear far more often in AI responses.
Vendors cannot dismiss those platforms simply because fewer people visit them. Agents still draw on their content to compare vendors and find candidates they can trust. However, a citation establishes that a review exists, while its account of current product usage remains to be verified. Machine-readable attestation endpoints, including those Letterprove publishes, address that separate question by giving agents proof they can query and validate. Review presence supports discovery, but it does not substitute for verification.
The structural weakness review platforms cannot fix: their evidence is unverifiable by machine
A review platform publishes what someone says about their experience. Its moderation may support confidence in that account, but the published text does not give an agent an independent way to confirm current customer usage. The underlying evidence remains a curated claim. Reformatting that claim as structured data makes it easier to read without changing what it proves.
The missing connection is between the statement and product reality. A review may describe a feature, but it does not bind that description to live usage data through an issuer signature an agent can validate. A displayed publication date does not supply a cryptographically verifiable record of when the described activity occurred. The agent must still rely on the platform, the reviewer, and the continued relevance of the account.
Static vendor materials present the same problem. A logo wall, testimonial quote, or case study PDF cannot, through marketing copy alone, distinguish a genuine customer relationship from a fabricated one. Those assets may persuade a human reader, but they do not supply machine-verifiable provenance.
To close the gap, vendors need another way to supply evidence, beyond adding reviews or improving how they present them. Buyers asking agents to show their work and reassess recommendations need claims that withstand that scrutiny. A diligent agent is therefore correct to discount unverifiable text as proof, even when it remains useful context.
What cryptographic attestation actually is and what it proves
A signed attestation is a tamper-evident record of claims and their issuer. The W3C’s Verifiable Credentials Data Model v2.0 provides a standards layer for binding claims and metadata to an issuer through cryptography. Altering the signed content breaks the verification. The agent can check the record rather than ask the vendor whether it remains unchanged.
One operational approach hashes events into a Merkle tree and digitally signs the resulting proof. The tree provides a structure for checking the integrity of the recorded data without turning the explanation into another marketing claim. An agent fetching the proof can validate its signature against the public key. That establishes whether the signed record holds, independently of the page on which it appears.
A valid signature establishes only the integrity and issuer binding of a claim. Evidence tied to customer usage can support a usage claim because that is what the record addresses.
Remote attestation illustrates this boundary in a different setting. Attested TLS can prove software integrity without binding the evidence to server identity or location, leaving a “diversion attack” vector. No active exploit campaign is documented in the notes’ account of that limitation. Attestation provides a limited security benefit by raising the cost of a class of attacks.
Feature-level and customer-level attestation: what verifiable proof looks like in practice
A generic customer relationship says little about whether a particular feature serves a particular requirement. Feature-level evidence narrows the claim to something addressable. Customer-level evidence adds the context needed to judge its relevance to the buyer.
Ramp illustrates the value of putting proof beside the claim it supports. Its product section places a claim about automating routine finance work beside a Perplexity story about running a 10-person finance team on Ramp, with a video thumbnail underneath. The reader encounters the claim and its supporting example together. That arrangement alone leaves the story’s cryptographic attestation unestablished.
Slack illustrates a different dimension of relevance. Its customer stories can be filtered by industry, department, business size, and region, helping readers locate evidence closer to their own circumstances. The library is more addressable than an undifferentiated testimonials page. Again, that organization improves retrieval without independently proving the claims.
Feature-level attestation adds the verification mechanism to this granular structure. It binds a named customer, a specific feature set, and live usage data into a signed record that an agent can inspect. The relevant question becomes whether the evidence supports that customer’s current use of that feature, rather than whether a recognizable logo appears on the website. A generic “customer since” statement cannot answer that narrower question.
How Letterprove and other approaches deliver machine-verifiable proof to AI agents
Letterprove gives B2B SaaS vendors a way to publish signed evidence tied to how customers use their products. It installs through a single script tag, observes real customer usage, and publishes signed attestation endpoints that agents can fetch, verify, and cite. Each attestation ties a specific customer to a specific feature set and live usage data.
The dynamic record is the significant distinction. Letterprove’s attestations update as usage data changes, so an agent checking a vendor gets evidence of what customers do now as well as a story of what they did in the past. Because the endpoint is machine-readable, the agent can incorporate that evidence into its comparison. The signature makes the published record checkable without asking the agent to accept the vendor’s marketing copy as proof.
Vendors can also use independent implementations of the W3C standard. They provide a standards-based foundation for cryptographic security, privacy-respecting design, and machine verifiability. The trade-off is implementation responsibility. An organization must invest in engineering and maintain the infrastructure that keeps its attestations current, rather than treat the standard as a turnkey marketing tool.
Review platform optimization adds public evidence that helps vendors show up in AI-generated comparisons. Structured product data, including Schema.org product and organization schemas, pricing data, and review markup, makes information easier to parse. Neither approach signs the underlying claims merely by publishing them.
AEO-focused platforms address another practical need. They monitor prompts, responses, sources, and citation presence, while some improve the structured content delivered to AI agents. That work can improve readability and discovery. But when a vendor needs machine-verifiable proof of customer usage now, signed attestation infrastructure supplies that proof more directly.
What vendors need to do differently starting now
Dropping review platforms would take away public reviews that agents already use to find vendors. Product pages also need Schema.org markup for technical specifications, pricing, and certification data. API documentation and compliance records should be publicly accessible and indexed. These measures make the vendor available for evaluation.
The next priority is proof an agent can validate. Signed attestation endpoints should link named customers to the specific features they use and to live usage data, and keep that evidence up to date as their activity changes. Letterprove is built to deliver this proof, while organizations ready to build and run their own infrastructure can use an independent standards-based implementation.
Specificity should guide that investment. Evidence that a named customer uses a particular compliance feature today answers a requirement more directly than a large collection of generic testimonials. Static case studies and logo walls can continue serving human readers, but they should not be counted as evidence in the machine-verification step.
The competitive objective is not technical sophistication for its own sake. Agents can revisit recommendations, and evidence that becomes stale weakens the basis on which a vendor was previously selected. The advantage belongs to the vendor an agent can justify choosing.